
The U.S. announced over the weekend it had reached the parameters of an agreement to end the war with Iran that started back in February.
But if you ask John Doyle, the end of hostilities isn’t likely to end Iran’s efforts to cripple countries it counts as enemies. Iran, which Doyle said began attacking other nations digitally since before the pandemic, is not going to stop those efforts.
Speaking via Zoom to the audience at the 11th annual Cyber-Physical Systems Security summit Tuesday at Oakland University, Doyle, director of Palo Alto Networks Unit 42, pointed out that Iran’s cybersecurity efforts started “roughly around 2020” between Israel and Iran.
Since the start of the war, Doyle said, the cybersecurity community has observed a sustained series of cyber operations from Iranian threat actors in response to U.S.and Israeli military operations.
“It has become more over the two countries pretty much going after each other and trying to undermine each other in any way possible,” Doyle said. “The cyber component comes into play way acutely when we’re looking at things roughly 2020 time frame six-ish years ago.”
Sponsored by the National Defense Industrial Association Michigan Chapter, CPS3 brought military, industry, government and academic experts to Oakland University for two days of discussion centered on the fast-changing threats facing critical infrastructure, defense systems and connected technologies.
Co-chairs Jennifer Tisdale and Dariusz Mikulski said this year’s program is designed around what they described as a more urgent threat environment, with sessions examining cyber conflict tied to geopolitical tensions surrounding the war with Iran, attacks on critical systems and the increasing role of artificial intelligence in both offensive and defensive cybersecurity.
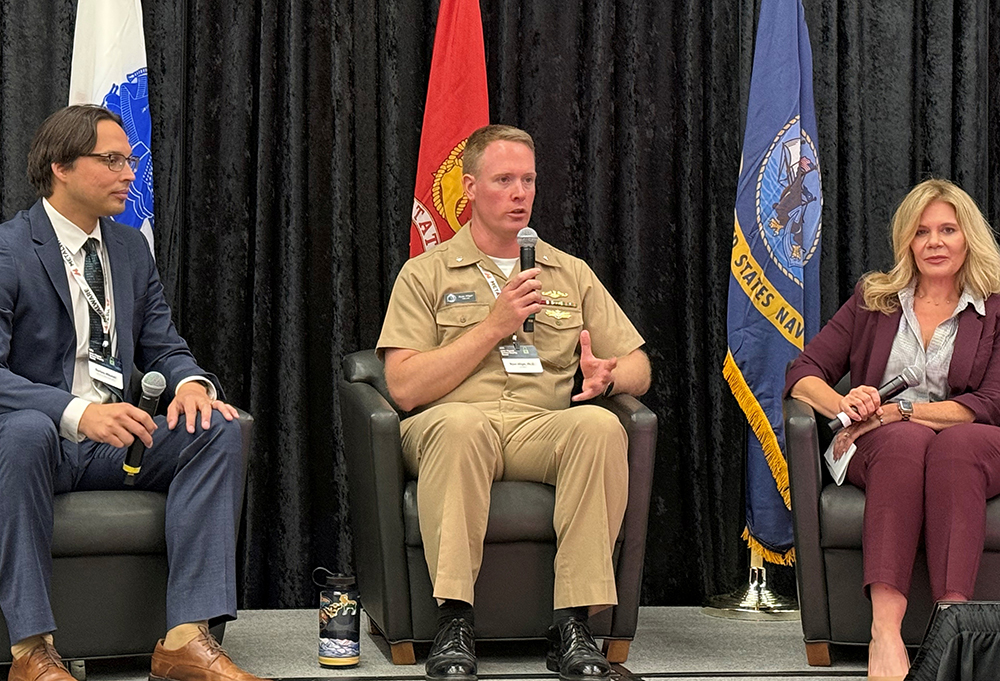
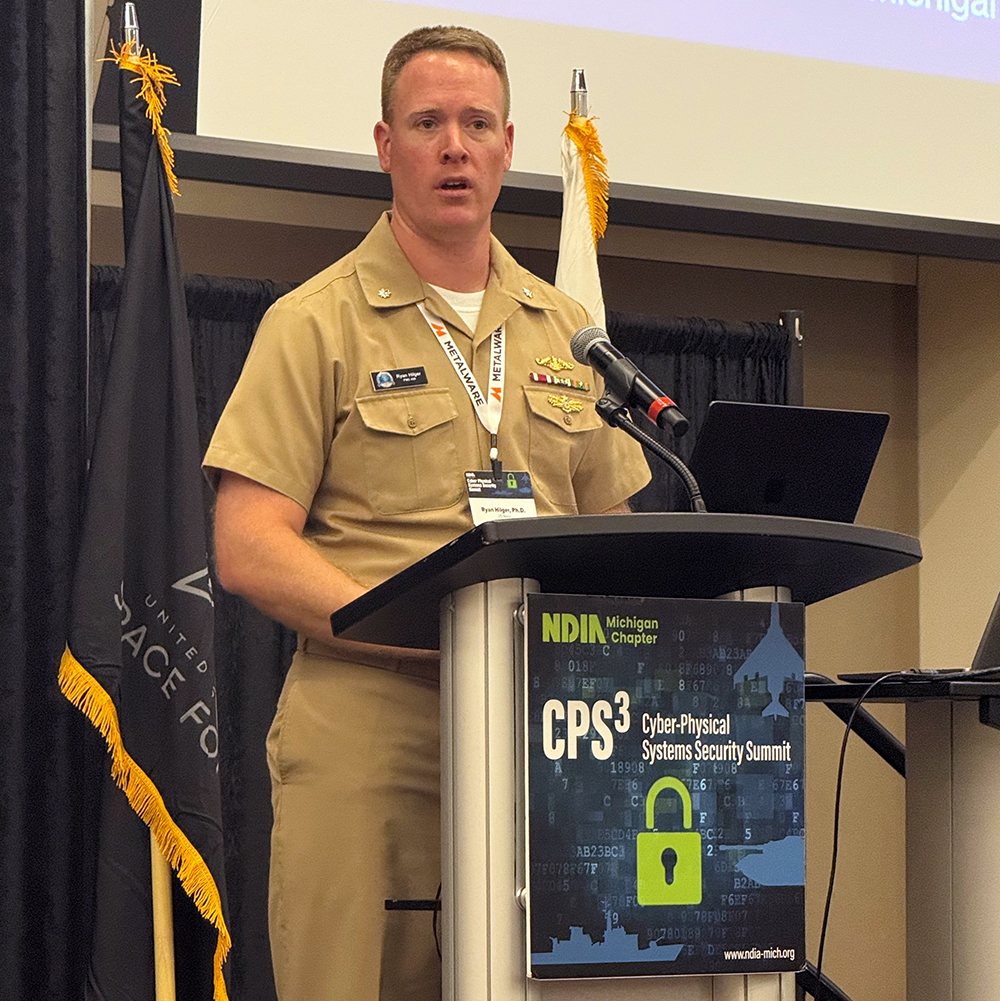
Sessions included a fireside chat featuring Ryan Hilger, Ph.D., principal program manager for the U.S. Navy, Doyle’s presentation on Iranian responses to “Operation Epic Fury” and a panel on foreign proximity threats to military and civilian assets.
Hilger focused his presentation on a May 2021 ransomware attack on the Colonial Pipeline, which operates the largest refined oil products pipeline in the United States, that targeted its computerized systems. The attack forced the company to halt all pipeline operations to contain the breach, leading to widespread fuel shortages and panic buying across the Eastern United States.
According to reports at the time, the attackers gained access to Colonial Pipeline’s network through a compromised password for an inactive virtual private network (VPN) account, which lacked multi-factor authentication. This vulnerability allowed the hackers to infiltrate the company’s IT systems and launch their ransomware attack.
“In Colonial’s operated operational technology, the systems that actually ran the pipelines were never directly compromised, but the active attackers were in the IT network,” Hilger said. “Colonial shut the pipeline down themselves out of caution because they didn’t know what they didn’t know.
“Colonial shut themselves down … The technical systems overall were fine,” he added. “The organization didn’t have a protocol for coping with that level of uncertainty so they made the most conservative decision available to them. And that decision cascaded through 18 states … and likely degraded military readiness across the East Coast, triggered a wave of policy responses that are still being felt five years later. That was not a technical failure. That was an organizational fear that happened to involve a computer.”
Tisdale said one of the defining differences this year is how prominently artificial intelligence was featured in the program.
“Rather than focusing only on traditional cyber tools and tactics, the summit will examine how AI is accelerating both attacks and defenses and forcing practitioners to respond faster to a growing volume of threats,” she said.
Co-chair Dariusz Mikulski said that reality is making cyber-physical security a broader public concern, not simply a defense issue.
“One of the summit’s priorities is helping attendees understand that cyber threats no longer stay confined to computer networks,” Mikulski said. “They can have immediate consequences for physical systems people rely on every day. The potential effects of attacks on power systems, water treatment facilities and other infrastructure are examples of why the summit will emphasize threats that can move quickly from the digital realm into everyday life.”
The event is also intended to connect defense-focused cybersecurity conversations with Michigan’s commercial strengths in automotive, manufacturing, mobility and emerging technology.
“Many of the issues discussed in military and government settings also have implications for civilian industries, particularly as vehicles, factories and other systems become more software-driven and interconnected,” Tisdale said.
Wednesday’s keynote panel featured a discussion about aligning federal ambition with state-level action and exploring how to bridge the gap between federal and state authorities while ensuring the integrated strategy provides clear protocols for responding to gray-zone cyber operations that fall below the traditional threshold of armed conflict.
The panel was chaired by Michael Stone, a partner with Warner Norcross + Judd LLP, who pointed out that most policy in this area is federal, states have “a strong interest in cyber policy.”
“We brought together a group of people that have all worked together at the federal and state level in cyber policy,” Stone said. “Michigan … was a national leader of the National Governor Association advocating for inputs from the states in cyber policy. Hopefully people will walk away and give a little more thought and hopefully give inputs because we have an obligation, I think, audiences of groups like this, to give input to our elected officials about what matters and why.”
After two days of a summit that brought out hundreds of attendees, Tisdale said she hopes people walk away from the event “understanding our world aren’t as ‘siloed’ as they like to believe they are.”
“We are very interconnected between aerospace, maritime, automotive and military,” she said. “Being able to put names to those faces and understand those roles in each entity and how they can work more collaboratively together … If they walk away with that, I will feel it was a successful two-day event.”

